Today, the Council agreed its position on the proposal to simplify certain rules on data protection, privacy and cybersecurity, while maintaining strong levels of protection for personal data. The changes aim to make the EU’s digital rulebook clearer and easier to apply for businesses, public administrations and citizens, to support EU competitiveness
The proposal forms part of the so-called ‘Omnibus VII’ legislative package in the EU’s simplification agenda. The package includes measures to simplify the EU’s digital legislative framework and the implementation of harmonised rules on AI. For the latter AI-related part, the legislative act was adopted on 29 June 2026.
Simplifying and streamlining the EU’s digital rulebook will make it easier for businesses to operate across Europe, reducing administrative burdens while maintaining high standards for data privacy and citizens’ rights. The Irish presidency has worked to secure a timely agreement in Council so that these improvements can start delivering real benefits sooner. This is an important step in ensuring Europe remains an attractive place to invest, innovate and grow trusted digital businesses.
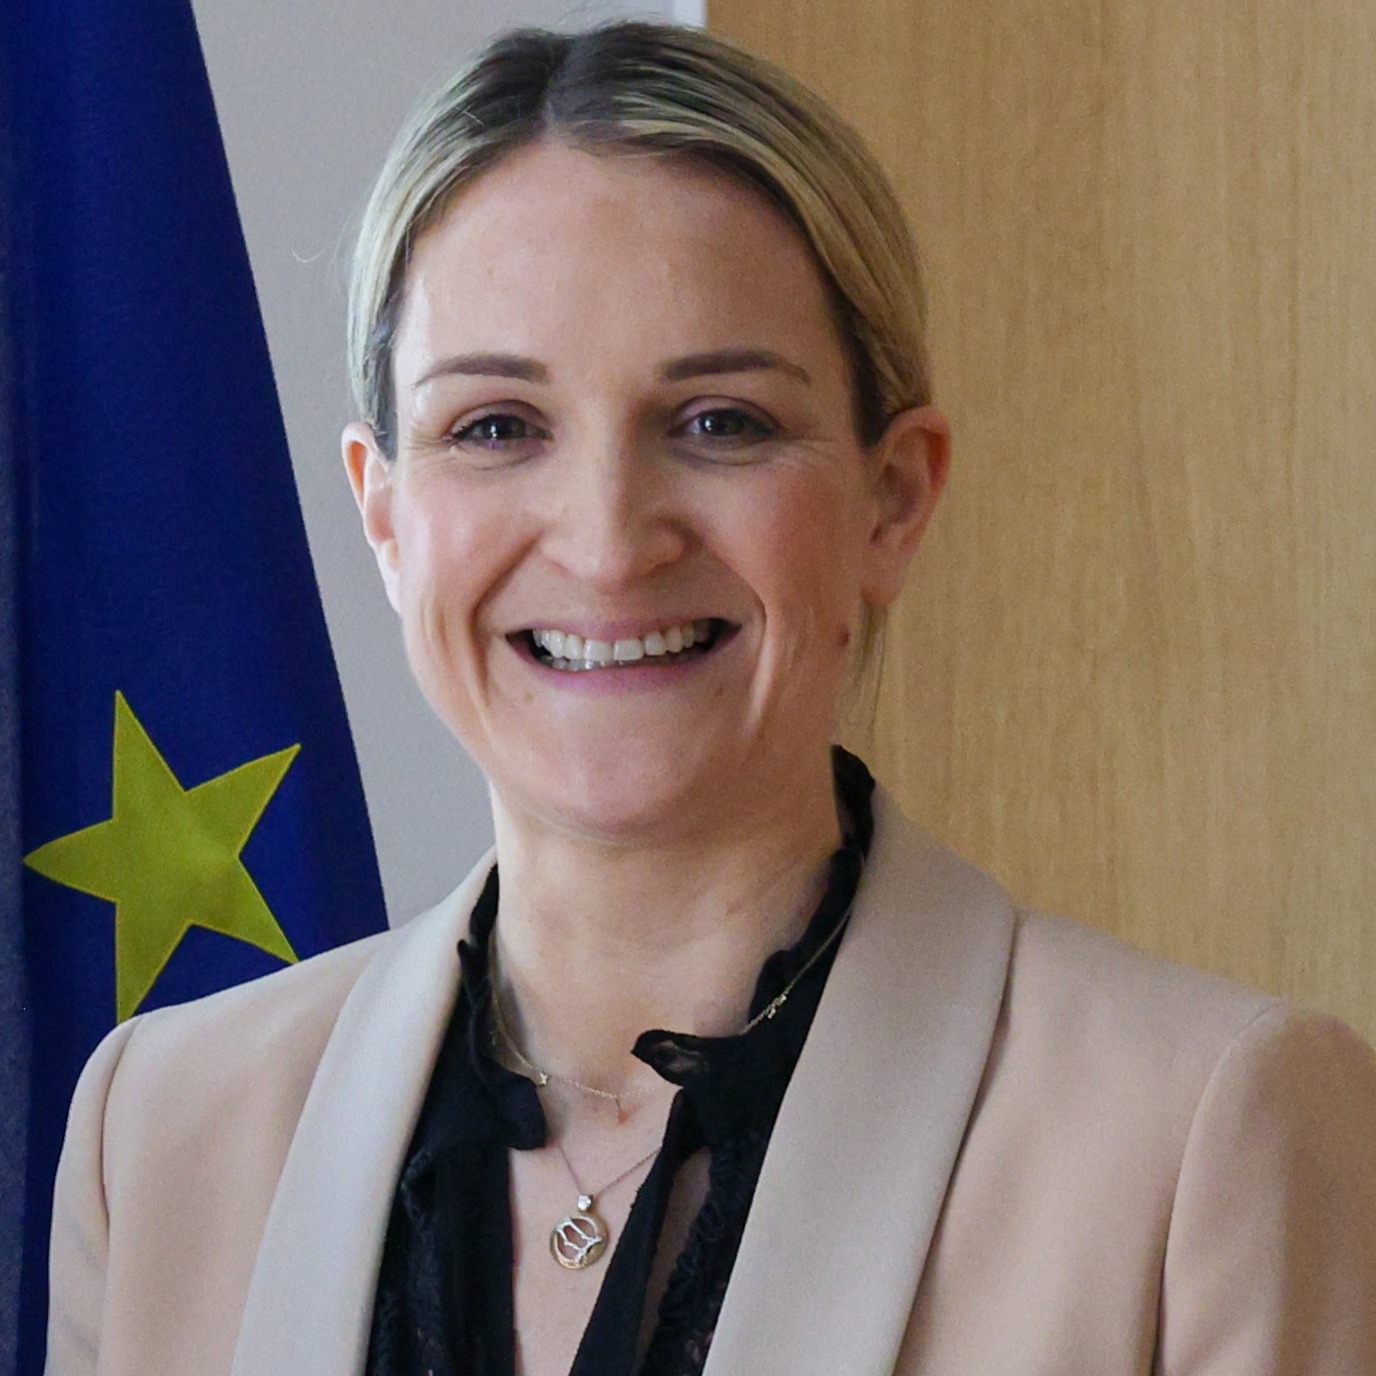
Helen McEntee, Minister for Foreign affairs and trade of Ireland
Under the Irish presidency, action is being taken under the Digital Omnibus to simplify rules on data protection, privacy and cybersecurity for businesses, public administrations and citizens, while maintaining established policy goals. These measures will reduce compliance costs and boost competitiveness and innovation. This is a key deliverable under the ‘One Europe One Market’ Roadmap and the Council is ready to engage in negotiations with the European Parliament as soon as it has established its position.
Thomas Byrne, Minister of State for European affairs and defence of Ireland
Main elements of the mandate
The proposal introduces amendments to the general data protection regulation (GDPR), modernises cookies rules laid down in the e-privacy directive, repeals provisions of the platform to business (P2B) regulation, consolidates single-market rules on data (the so-called ‘data acquis’), and introduces a mechanism for a single reporting point for cyber security and data incidents.
GDPR
Building upon the Commission proposal, the mandate includes a series of amendments to the GDPR, which seek to simplify and streamline provisions while maintaining appropriate protection for fundamental rights.
First, the Council mandate maintains the current definition of personal data and introduces a new provision on pseudonymisation and the identification of a natural person, with a view to helping companies comply with their GDPR obligations by clarifying rules in this area. Compliance rules are also being simplified in relation to unfounded or excessive requests and specific low risk circumstances in relation to information obligations.
The Council supports the introduction of a principle-based definition of ‘scientific research’, facilitating the consistent application of processing of personal data for this purpose and introducing targeted exemptions to certain obligations so that research organisations can operate in a simplified framework when it comes to data protection.
Furthermore, the Council mandate introduces safeguards to the newly proposed derogation allowing for the processing of sensitive data for the purpose of biometric verification and in the context of the development and operation of AI systems. Innovation and the development of AI are further supported with clarifications on the lawful ground for processing personal data and need to maintain appropriate safeguards.
The Council also backs the Commission proposal to extend the deadline for the notification of personal data breaches, as well as other measures to facilitate GDPR compliance and ensure greater consistency. Such measures include a single list at EU level of categories of processing likely to result in a high risk for individuals or the establishment of common templates for organisations to fulfil their regulatory obligations.
Data acquis and trade secrets
The mandate consolidates and streamlines rules on data altruism and data intermediation services. It presents benefits for public administrations holding public sector data, as well as for re-users, as they can streamline processes and reduce the administrative burden associated with interpreting and implementing diverse national laws.
The mandate introduces the possibility for public sector bodies to set out different conditions and charge higher fees for the re-use by very large enterprises and, in particular, undertakings designated as gatekeepers. It also answers to the urgent need to strengthen safeguards against the risk of trade secret leaks to third countries. The mandate specifically provides that trade secrets would have to be disclosed only once the data holder and the user have taken all necessary measures to preserve their confidentiality.
e-privacy directive and cookies
The Council mandate maintains the rules on cookies and other kinds of online tracking technologies under the e-privacy directive. This framework is updated with clearer and additional purposes where consent will not be required for the placing of cookies on a user device, thus reducing the number of cookie banners when navigating online. This would apply, for example, when necessary for the provision of a service, for the purpose of audience measurement or for ensuring the security of the user’s device.
The mandate also amends certain provisions related to the regulation on the protection of natural persons regarding the processing of personal data by the EU institutions, bodies, offices and agencies and on the free movement of such data (EUDPR) aligning them with the changes proposed under the GDPR.
Reporting cybersecurity and data incidents
The Council mandate replaces the proposed single-entry point at EU level by the establishment of a national entry point in each member state, supporting and facilitating the reporting of incidents and related events under different EU laws.
Furthermore, the Council mandate proposes the establishment of an incident reporting information point at EU level, as well as specific provisions towards a harmonised framework for incident notification and on cross-border incident notifications.
Next steps
Following today’s approval of the Council’s mandate, the Council presidency will start negotiations with the European Parliament once the latter adopts its own negotiating position with a view to a speedy agreement on the file.
Background
In October 2024, the European Council called on all EU institutions, member states and stakeholders, as a matter of priority, to take work forward, notably in response to the challenges identified in the reports by Enrico Letta (‘Much more than a market’) and Mario Draghi (‘The future of European competitiveness’).
Since February 2025, the Commission has put forward twelve ‘Omnibus’ packages aiming to simplify existing legislation, including a seventh Omnibus consisting of two proposals, one aiming to simplify the EU’s digital legislative framework and one aiming to simplify the implementation of harmonised rules on AI.
The ‘One Europe, One Market’ roadmap signed by the presidents of the Council of the EU, the European Parliament and the Commission on 24 April 2026 in the margins of the informal leaders’ meeting in Nicosia includes the objective of concluding work on all simplification packages by the end of 2027.